Cyber Attacks
Cyber Incident Response Team: 10 Critical Questions Answered
Your response team’s greatest vulnerability is not external intrusion but internal coordination failure during high-pressure decision-making windows.
Your response team’s greatest vulnerability is not external intrusion but internal coordination failure during high-pressure decision-making windows.
Open redirects hide in valid URL patterns, making them invisible to standard input validation and requiring behavioral analysis to uncover.
BitLocker protects lost hardware but fails to stop attackers who already have access to your running system or remote management tools.
Digital forensics does not stop an attack; it reconstructs the timeline of events to prove liability, scope, and root cause after the breach is contained.
FileVault uses hardware acceleration to encrypt your entire drive on the fly, meaning your data remains secure even if the physical disk is stolen, without impacting daily performance.
Small teams often ignore that mobile devices bypass network perimeter defenses, requiring device-level controls that standard firewalls cannot provide to protect corporate data.
Choosing between these protocols determines whether your email data lives on a single device or persists across your entire digital infrastructure.
Most command and control traffic masquerades as normal web browsing, making it nearly impossible to stop by blocking specific IP addresses alone.
Unsupported hardware bypasses software defenses by exposing low-level execution paths that vendors no longer patch or monitor.
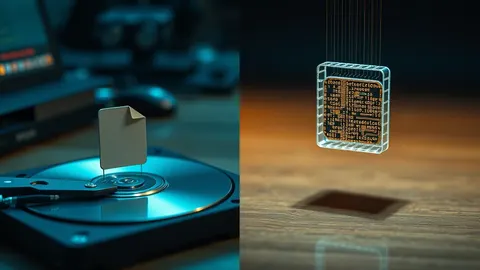
Droppers write persistent files to disk while loaders execute payloads in memory, creating distinct forensic signatures and detection challenges.
Running suspect code in isolation reveals hidden behaviors that static checks miss, but clever malware detects and hides from these environments.
Coordinated disclosure shifts security from a race against attackers to a structured negotiation between reporters and vendors to fix flaws before exploitation.
Credit monitoring tracks exposure indicators, not real-time transactions, leaving a window where fraud occurs before alerts trigger.
Physical isolation does not prevent logical compromise when management interfaces remain exposed to the same network segments as user traffic.
Reducing access rights exposes hidden application errors and forces developers to design systems that fail safely when components are removed or restricted.
Dynamic testing often misses logic errors because it treats applications as black boxes, requiring manual validation to confirm that a finding is actually exploitable in your specific environment.
Tokenization replaces sensitive data with random strings that hold no mathematical relationship to the original value, ensuring that even if the database is stolen, the data remains useless.
SAML transfers identity assertions, not passwords, creating distinct trust boundaries that most administrators fail to isolate or validate correctly.
Credential leaks often hide in plain sight within normal authentication logs, requiring you to correlate disparate signals rather than rely on single-point alerts.
Attackers exploit the gap between your email security and your payment verification, turning routine administrative tasks into high-value financial losses.
Your security boundary ends where your vendor begins, making their weak controls your immediate liability.
Understanding whether a threat requires human action to move reveals how to isolate the breach before it consumes the network.
Fine-tuning changes model weights to learn patterns, while retrieval-augmented generation keeps weights static and fetches facts at query time to ensure accuracy.
Generative models erase the grammatical errors and awkward phrasing that once served as the primary warning signs of social engineering attempts.